
Corellium Falcon
Mobile Vulnerability
Research Solutions

Provides government organizations and researchers with the mobile vulnerability research, exploit introspection, and malware analysis not possible on physical iOS and Android devices.
Corellium Falcon
Capabilities

On-Demand Access
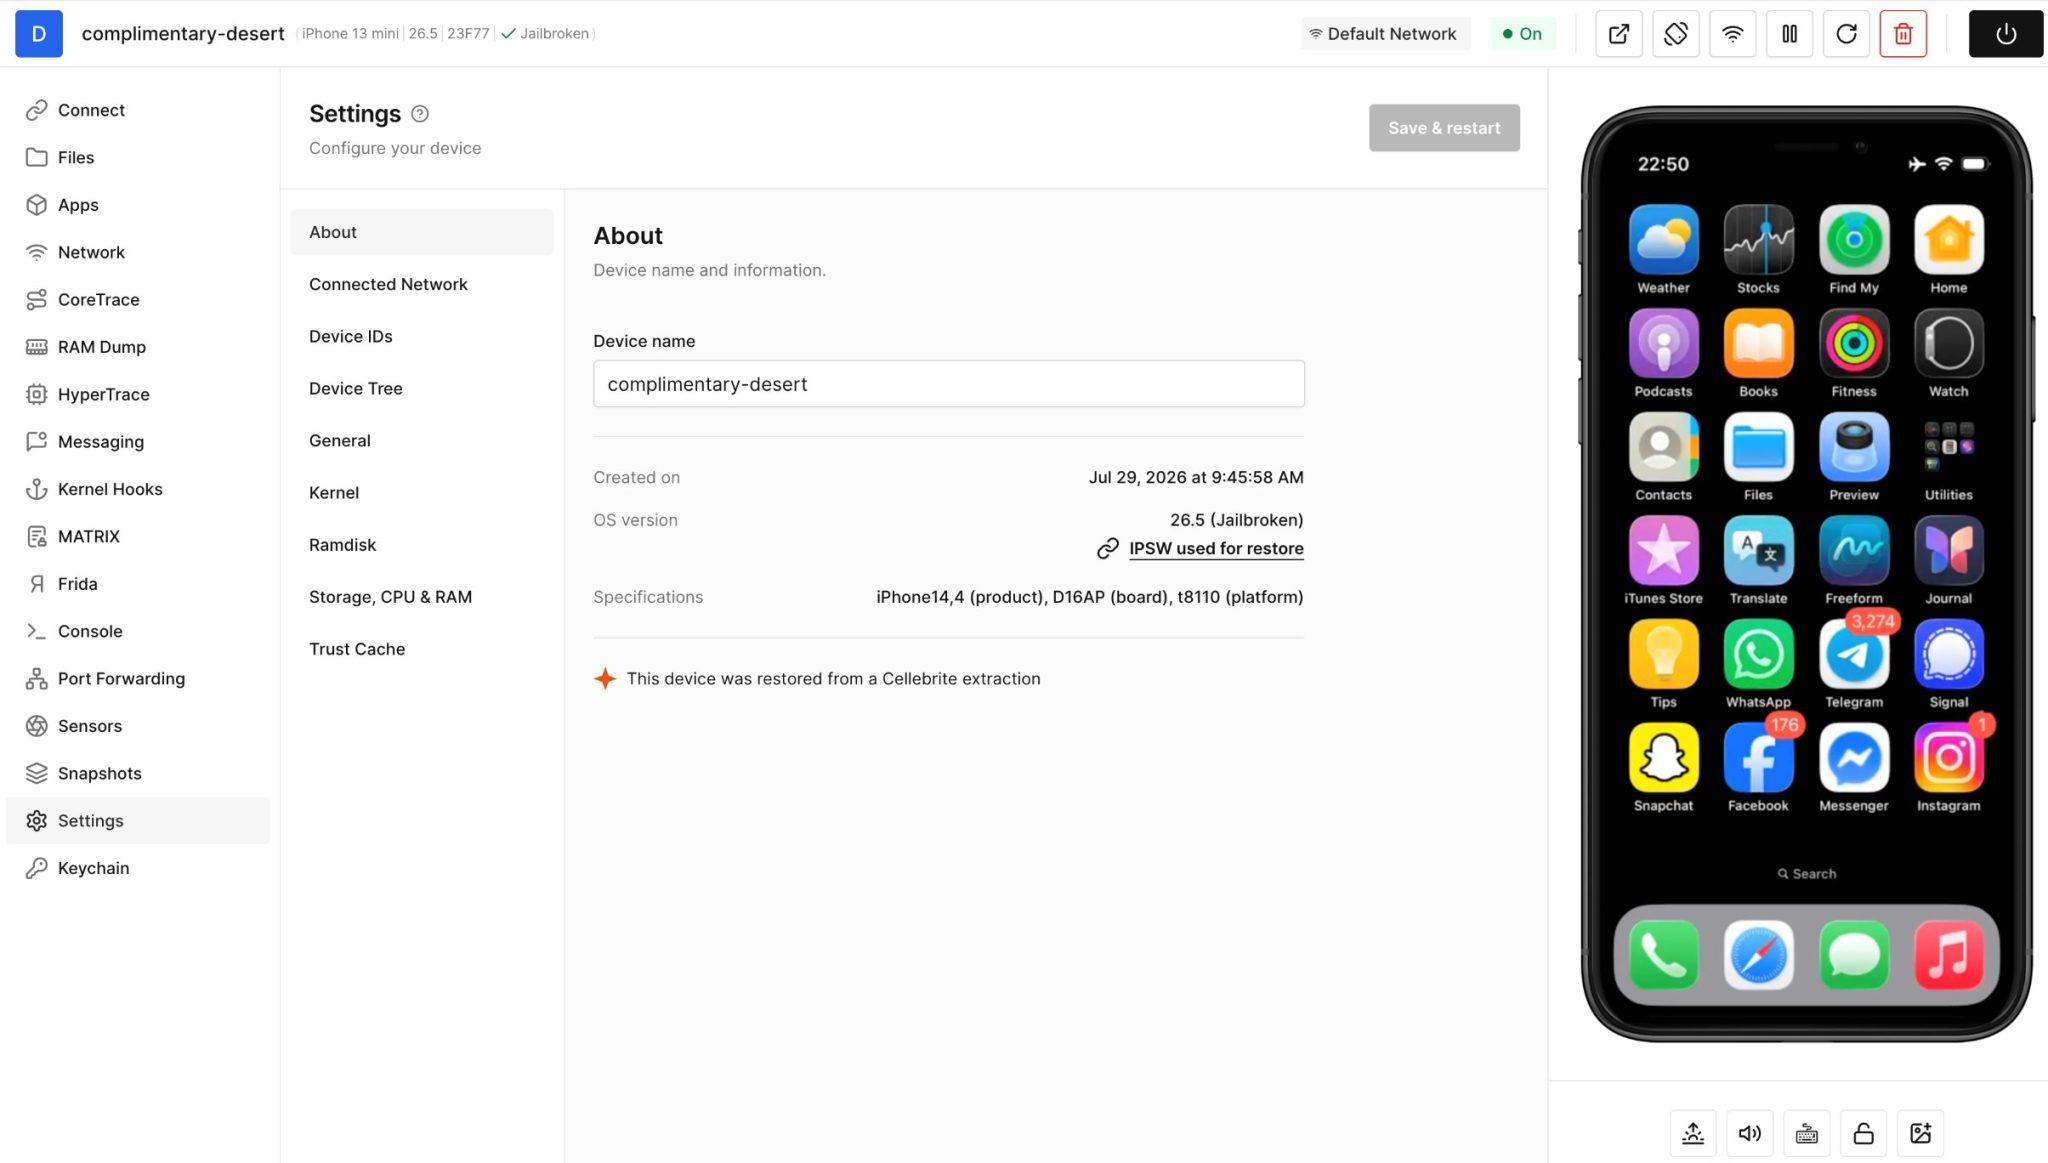
Spin up iOS, iPadOS and Android devices across supported OS versions and device models, including the latest releases. Get root and kernel access with built-in research tools designed for advanced security testing and mobile research.

Powerful Introspection
See what is happening across the OS kernel, processes and subsystem I/O. Inspect logs, file systems, system calls and network traffic in real time. Run scripts and use debugging tools through the integrated Frida console.

Kernel Debugging
Perform advanced security research with deep control over the kernel and boot process. Modify patches, device identifiers, trust caches and device trees. Use kernel hooking, program flow tracing and coverage tracing to investigate system behavior and vulnerabilities.

Snapshots & Cloning
Capture and clone device states at any point in your research. Pause and resume firmware and application activity, then restore previous states to reproduce findings and repeat testing. Share consistent environments across teams to simplify validation and collaboration.
Falcon Mirror Add-On
Start with a Device State Your Research Requires
Falcon Mirror Add-on lets researchers import supported Inseyets extractions into Falcon, giving them a faster starting point for advanced analysis without rebuilding that device context manually.
Move Beyond Pristine Device States
Corellium Falcon
Solutions
Mobile Vulnerability
Research Solutions
Research vulnerabilities across iOS, iPadOS and Android with deep system visibility and introspection. Use high-fidelity virtual devices to investigate vulnerabilities, analyze system behavior and validate exploits in a controlled and repeatable environment.

Malware Analysis
Analyze suspicious applications and mobile threats across iOS, iPadOS and Android. Detonate malware in a controlled environment, collect indicators of compromise, inspect runtime behavior and investigate how threats interact with the operating system.

App Pentesting
Perform static and dynamic testing without relying on physical device labs. Give security teams repeatable access to mobile environments for application analysis, pentesting and verification across distributed teams.

Operational Training
Deliver hands-on mobile security training in consistent, repeatable environments. Give instructors and participants browser-based access to the same device configurations without managing or shipping physical devices.
Editions
Malware & Threat Research
App Pentesting
Introspection & Reversing
Exploit Analysis & Verification