
Cellebrite UFED:
The Widest Access to the Latest Mobile Devices
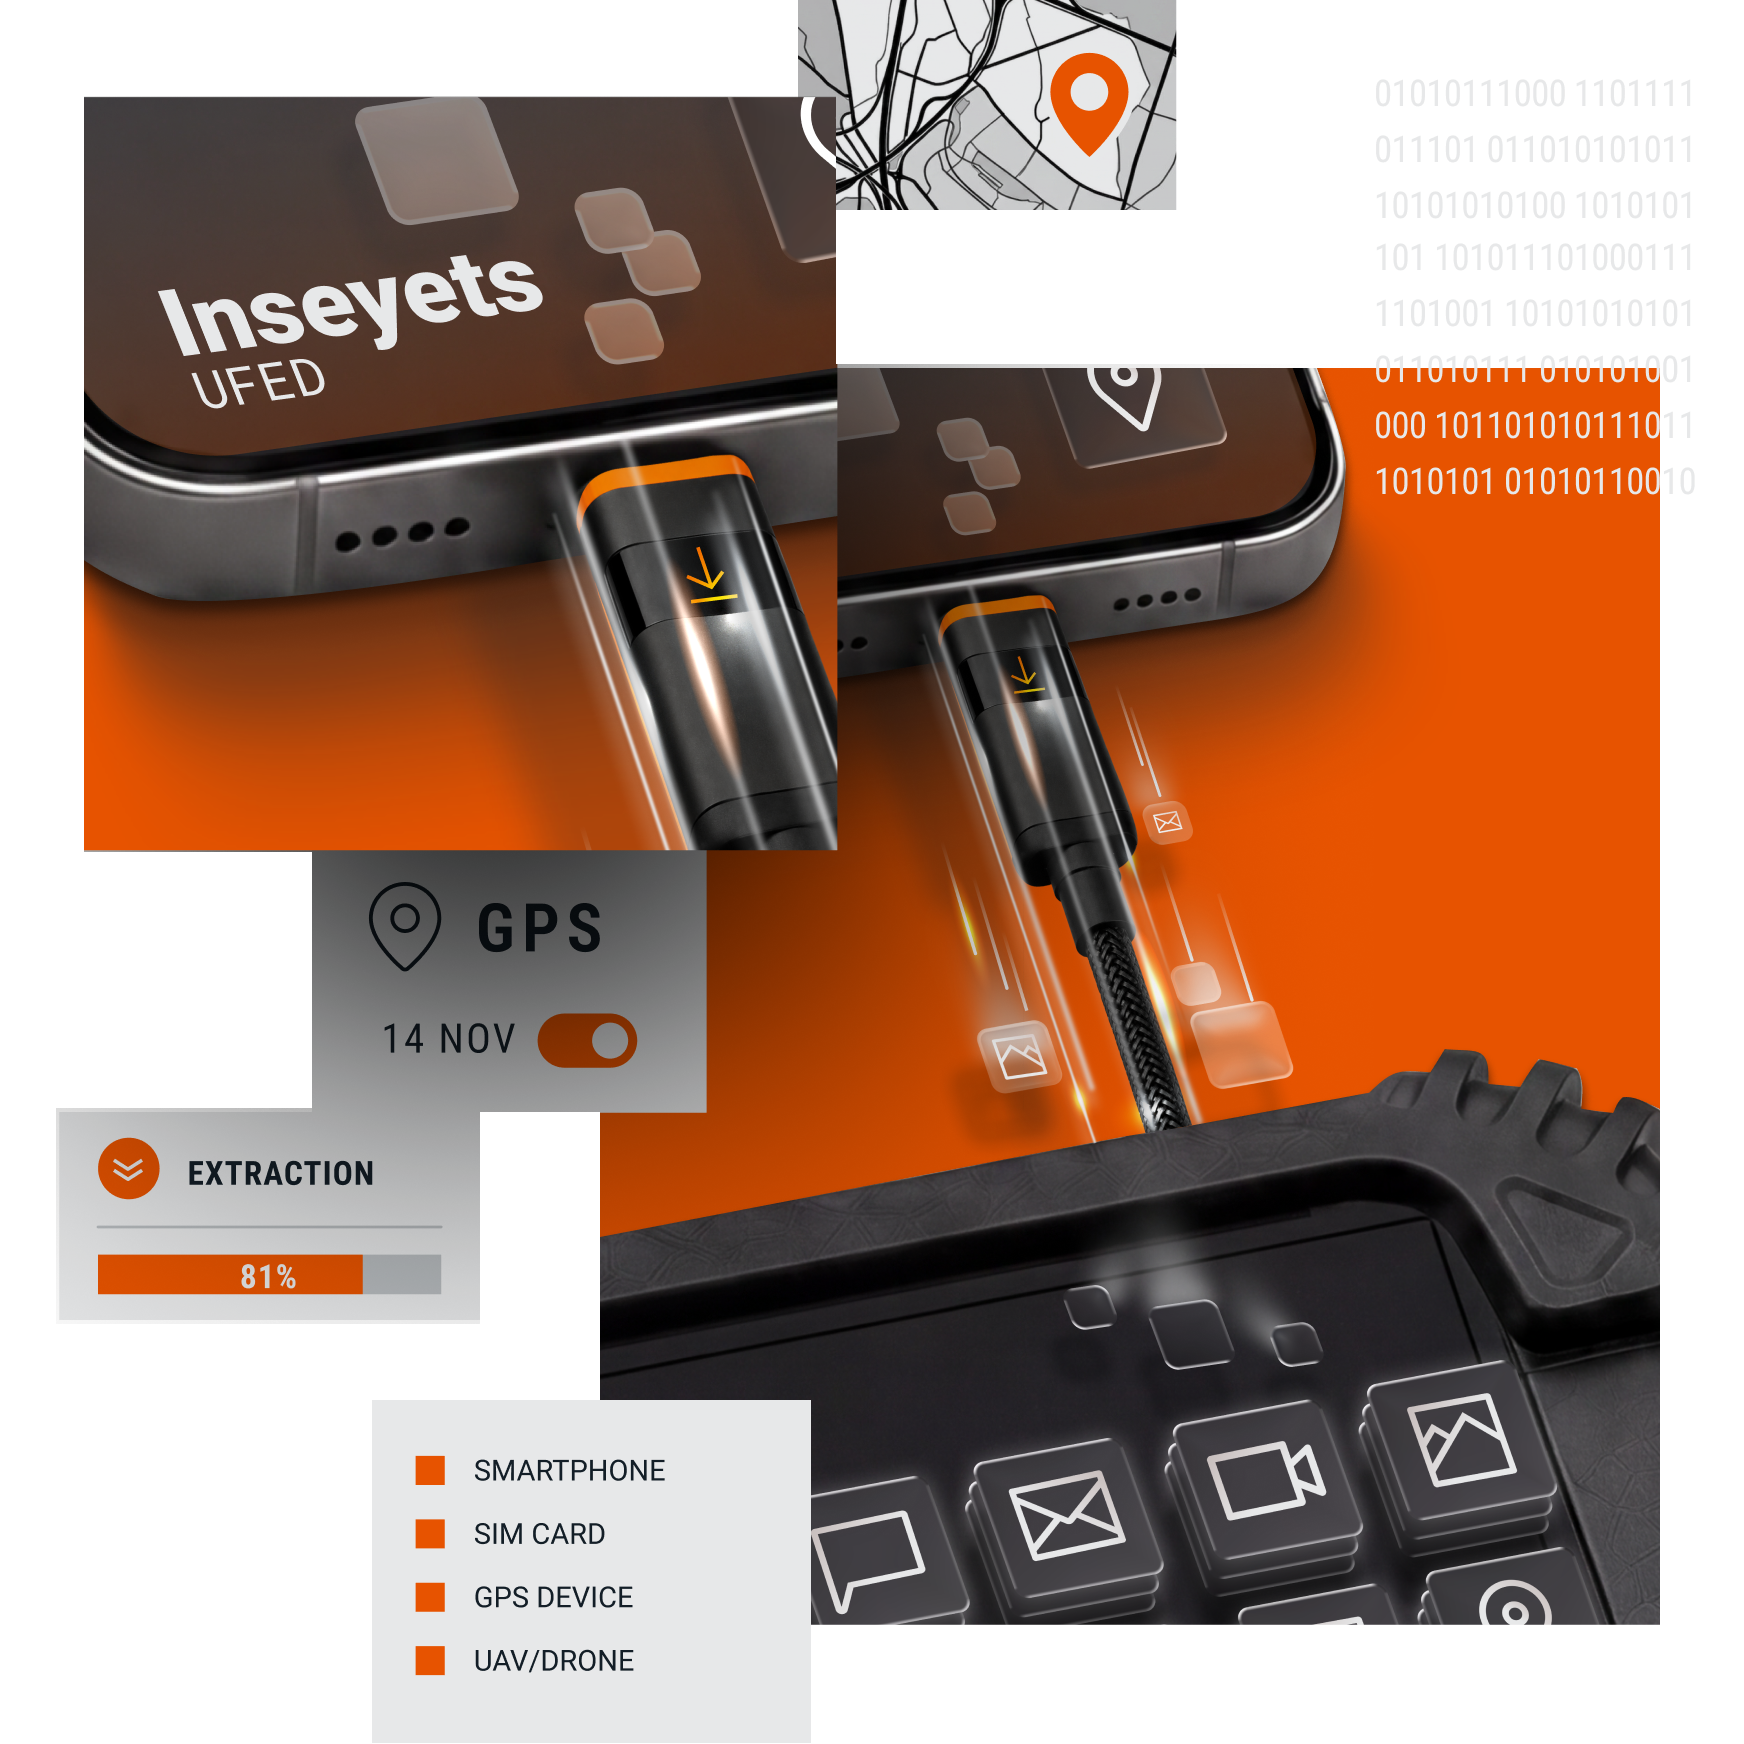
Cellebrite UFED is the access and extraction engine of the Cellebrite Inseyets suite, delivering Full File System data from the widest range of iOS and Android devices.
BROADER DEVICE ACCESS THAN OTHER EXTRACTION TECHNOLOGY
OF NATO COUNTRIES TRUST CELLEBRITE
FASTER EXTRACTION SPEED
Locked Mobile Devices
Shouldn't Mean Dead Ends
Encryption locks out more than it used to.
Modern devices default to encryption, and a growing share of the data investigators need -- messages, app data, deleted files -- sits behind it. Tools that only handle logical extraction leave that evidence out of reach.
Not every case can wait for the lab.
Devices seized in the field often need triage before an examiner ever sees them. Without a way to preview a device on the spot, teams either wait or risk mishandling evidence.
One tool, hundreds of device configurations.
Every manufacturer, OS version and security patch changes what's reachable. A device access engine that isn't updated constantly falls behind the devices investigators actually seize.
Extraction is only half the job.
Getting data off a device means nothing if it can't move cleanly into decoding and analysis. Disconnected tools mean manual handoffs and duplicate work.
Chain of custody starts at extraction.
If the access method isn't defensible, nothing downstream is either. Evidence has to be captured in a way that holds up in court from the first connection.
Built for Teams That
Can't Wait for Access
Law Enforcement
Devices seized in the field or in the lab need fast, defensible access. UFED gets examiners past locks and encryption quickly, with Full File System extraction that turns a seized phone into a case-ready evidence file in the same format examiners already defend in court.
Enterprise & eDiscovery
Corporate investigators and eDiscovery teams need targeted, defensible collection from employee devices without overreaching. UFED's flexible extraction options -- from advanced logical to Full File System -- collect what a case requires while respecting scope and privacy requirements.
Defense & Intelligence
When a device is captured in the field, the data on it has a shelf life. UFED extracts GPS data, communications and app data at the point of capture, disconnected and field-ready, before the operational value of that data expires.
Corrections & Border Security
Contraband devices and border seizures require access without a lab connection. UFED's field-ready configurations let frontline teams extract data on-site, feeding straight into Inseyets for deeper analysis.
The Numbers
Behind the Access
BROADER DEVICE ACCESS THAN OTHER EXTRACTION TECHNOLOGY
OF U.S. FEDERAL DEPARTMENTS USE CELLEBRITE
PUBLIC SAFETY, ENTERPRISE, AND GOVERNMENT CUSTOMERS WORLDWIDE
What Can UFED Do?
UFED Is the Front Door to the Cellebrite Digital Investigation Platform
UFED is the access and extraction layer of the Cellebrite Inseyets suite, and the front door through which every case begins. From the moment a device is seized, evidence flows automatically into decoding, case management and cross-case analysis, with no manual handoffs or re-entered data.
Physical Analyzer
Decode and analyze every UFED extraction, with AI-assisted review, geolocation mapping and court-ready reporting.
Genesis
Review digital evidence, surface relevant leads, connect information across multiple evidence sources and move through cases faster with Cellebrite’s AI-powered investigation solution.
Guardian
Manage evidence, chain of custody and cross-team collaboration from extraction through case closure.
Pathfinder
Correlate Inseyets data with mobile and digital evidence across cases to surface leads and identify networks.
Every Environment, From Lab to Line
Inseyets powers the full range of Cellebrite hardware -- from station-based kiosks for self-service extraction to ruggedized field devices built for the most demanding operational environments.
Covert Forensic Imaging Device (CFID)
Palm-sized and battery-powered for forward-operating environments. UAV/drone capable, with SIM card extraction, iOS and Android support and VPN connectivity -- built for missions where the lab can't come to you. Link:
Learn More About CFIDCellebrite Tactical Extraction Kit (C-TEK)
Field-Ready Bundle Ruggedized, mission-ready package for forward-operating defense that combines Inseyets-powered extraction hardware, cables and charging accessories configured for rapid deployment in harsh and disconnected environments.
Learn More About C-TEKCellebrite Kiosk
Self-Service Station Brings the full Inseyets extraction and decoding capabilities to frontline officers with no forensics background. Deployed in law enforcement, corrections and border environments for simple, guided mobile device extraction in minutes.
Learn More About KioskFly Away Kits
Rapid Response Kit Self-contained, airline-transportable deployment kits for rapid response teams and surge capacity deployments. Everything needed to stand up full Inseyets extraction capability at any location, in hours, not days. Details coming soon.
Cellebrite UFED in Your Region
Every Locked Phone Is a Case on Hold
Across a patchwork of federal, state, provincial and county agencies,
the smartphone has become the evidence in nearly every North American case,
and default device encryption keeps raising the bar for getting into one lawfully.
Encryption Set the Clock Running
Since manufacturers shifted to default device encryption, the agencies without a lawful, defensible access method are the ones losing ground, not the people they’re investigating.
The Region With the Most to Unlock
North America reports the highest device lock rate of any region Cellebrite surveys, so a fast, defensible access method carries
more weight here than almost anywhere else.
One Network, Many Jurisdictions
A single case can run through a county jail, a state prison and a federal system at once. Moving fast on extraction is what keeps intelligence ahead of a network that doesn’t respect the same borders
investigators do.
One Continent, Many Legal Systems, One Extraction Standard
Cross-border cases are the norm in EMEA, not the exception, and GDPR governs how every device is handled from the moment it’s seized.
Extraction That Respects Data Minimization.
GDPR doesn’t just constrain what you can keep, it shapes what you should extract in the first place. UFED’s targeted and Full File System options let examiners scope collection to what a case needs.
Built to Cross Borders.
As cases move between one member state’s investigation and another’s court, evidence collected under one authority has to hold up when it changes hands. UFED’s chain-of-custody handling is built for that.
Institutional Diversity, One Tool.
Whether you run a centralized national service or your own force’s lab, UFED adapts to the structure you already have instead of asking you to rebuild around it.
Every Operating System, No Waiting for the Lab
From Five Eyes partners to fast-growing forensic programs across Southeast Asia and India, APAC agencies face the widest device and OS fragmentation of any region, and some of the largest distances between a field seizure and the nearest lab.
Distance Is the Enemy, Not the Device.
Where the nearest lab can be a flight away, UFED’s field and lab deployment options mean extraction doesn’t wait on geography.
An Android-First Region, an Android-Ready Tool.
With Android holding the majority of the region’s device share, broad, current OS and chipset coverage isn’t a nice-to-have here, it’s the baseline UFED is built to clear.
Fewer Locked Devices, Same Urgency.
APAC reports fewer locked devices than most regions, but that just moves the pressure downstream. Once access is solved, the case is only as fast as everything that comes after it.
The Network Moves Fast. Extraction Has to Move Faster
Across Latin America, cartel and gang operations increasingly run through smuggled and seized phones, and every hour a device sits unextracted is an hour the network keeps operating.
Every Seized Phone Is a Live Lead.
Commanders keep directing operations from a single handset. Fast, defensible extraction turns that seizure into the lead that stops the next shipment or act of violence, rather than just closing the door on one device.
Evidence That Holds Up Under LGPD.
Prosecutions have to respect Brazil’s LGPD and comparable regional data protection law while still delivering evidence that puts the people behind an operation in front of a court.
The Fastest-Moving Region in Digital Investigations.
Agencies across Latin America are reallocating resources toward digital investigations faster than anywhere else Cellebrite surveys. UFED’s field-deployable hardware is built to keep pace with that shift.
Every Locked Phone Is a Case on Hold
Across a patchwork of federal, state, provincial and county agencies,
the smartphone has become the evidence in nearly every North American case,
and default device encryption keeps raising the bar for getting into one lawfully.
Encryption Set the Clock Running
Since manufacturers shifted to default device encryption, the agencies without a lawful, defensible access method are the ones losing ground, not the people they’re investigating.
The Region With the Most to Unlock
North America reports the highest device lock rate of any region Cellebrite surveys, so a fast, defensible access method carries
more weight here than almost anywhere else.
One Network, Many Jurisdictions
A single case can run through a county jail, a state prison and a federal system at once. Moving fast on extraction is what keeps intelligence ahead of a network that doesn’t respect the same borders
investigators do.
One Continent, Many Legal Systems, One Extraction Standard
Cross-border cases are the norm in EMEA, not the exception, and GDPR governs how every device is handled from the moment it’s seized.
Extraction That Respects Data Minimization.
GDPR doesn’t just constrain what you can keep, it shapes what you should extract in the first place. UFED’s targeted and Full File System options let examiners scope collection to what a case needs.
Built to Cross Borders.
As cases move between one member state’s investigation and another’s court, evidence collected under one authority has to hold up when it changes hands. UFED’s chain-of-custody handling is built for that.
Institutional Diversity, One Tool.
Whether you run a centralized national service or your own force’s lab, UFED adapts to the structure you already have instead of asking you to rebuild around it.
Every Operating System, No Waiting for the Lab
From Five Eyes partners to fast-growing forensic programs across Southeast Asia and India, APAC agencies face the widest device and OS fragmentation of any region, and some of the largest distances between a field seizure and the nearest lab.
Distance Is the Enemy, Not the Device.
Where the nearest lab can be a flight away, UFED’s field and lab deployment options mean extraction doesn’t wait on geography.
An Android-First Region, an Android-Ready Tool.
With Android holding the majority of the region’s device share, broad, current OS and chipset coverage isn’t a nice-to-have here, it’s the baseline UFED is built to clear.
Fewer Locked Devices, Same Urgency.
APAC reports fewer locked devices than most regions, but that just moves the pressure downstream. Once access is solved, the case is only as fast as everything that comes after it.
The Network Moves Fast. Extraction Has to Move Faster
Across Latin America, cartel and gang operations increasingly run through smuggled and seized phones, and every hour a device sits unextracted is an hour the network keeps operating.
Every Seized Phone Is a Live Lead.
Commanders keep directing operations from a single handset. Fast, defensible extraction turns that seizure into the lead that stops the next shipment or act of violence, rather than just closing the door on one device.
Evidence That Holds Up Under LGPD.
Prosecutions have to respect Brazil’s LGPD and comparable regional data protection law while still delivering evidence that puts the people behind an operation in front of a court.
The Fastest-Moving Region in Digital Investigations.
Agencies across Latin America are reallocating resources toward digital investigations faster than anywhere else Cellebrite surveys. UFED’s field-deployable hardware is built to keep pace with that shift.
Everything You Need to Evaluate
and Deploy UFED
Cellebrite UFED: Every Device Has Data Worth Reaching
UFED gets your team past the locks, encryption and containers standing between you and the evidence — trusted by 93% of U.S. federal departments and 7,000+ public safety, enterprise and government customers worldwide.
Frequently Asked Questions
Cellebrite UFED (Universal Forensic Extraction Device) is the access and extraction engine of the Cellebrite Inseyets suite. It gets examiners into the widest range of iOS and Android devices and extracts Full File System data, including encrypted, locked and containerized application data.
UFED is the access and extraction component within Inseyets (Inseyets.UFED). Inseyets is the full suite, combining UFED’s extraction with Physical Analyzer’s decoding and analysis, plus Streamline, Triage, Quick View, Autonomy, UFED Cloud, Commander and Reader.
UFED supports advanced logical, Full File System and targeted data set extraction, so teams can match the collection method to what the case requires, from broad forensic capture to narrow, privacy-conscious collection.
Yes. UFED is built to access encrypted, locked and containerized application data that logical-only tools can’t reach. Unlocking capability is available as a separate package; UFED is unlock-ready but the unlock package is purchased separately.
UFED runs on computer-based hardware or a full field kit, and requires a Cellebrite Max dongle. It is not supported on Touch2; Touch3 requires an upgrade kit and isn’t optimal for full Inseyets capability.
A network connection is recommended for full capability, though no device data is exchanged over that connection. An offline configuration is available to match an agency’s security requirements.
Streamline moves an extraction from UFED directly into Inseyets.PA (Physical Analyzer) for decoding and analysis in a few clicks, without switching tools or re-entering data.
See the Inseyets Focus Hub for ongoing release updates.
Cellebrite Inseyets requires a Cellebrite Max dongle. (Check your dongle type here)
Cellebrite Inseyets.PA (version 10.x), operates on a database that handles large volumes of data. It introduces new features like Geo-Location Semantics, Media Origin, Import/Export and quicker case reopening. With the new Cellebrite Inseyets offering, you will also enjoy additional enhancements like Cloud and Crypto features. (Cellebrite Inseyets.PA and PA 7, share the same decoding abilities)
You may explore Cellebrite Inseyets powered by PA v10.x, however, please be aware that you will only be able to utilize the decoding and analysis features. The rest of Cellebrite Inseyets capabilities such as extraction and other advanced capabilities will not be available to try.


