
Cellebrite Inseyets:
One Suite. From Device to Actionable
Intelligence
Cellebrite Inseyets is an all-in-one digital forensics software suite. It accelerates digital investigations and intelligence by extracting and analyzing complex, encrypted data, surfacing relevant insights quickly and preserving forensic integrity at every stage.
CUSTOMERS WORLDWIDE
MORE DATA
FASTER TIME TO EVIDENCE
The Data Keeps Growing. Old Tools Can’t Keep Up.
Caseloads Outpace Your Team.
Every additional encrypted app, cloud account and gigabyte of data adds hours to a workflow that hasn’t scaled to match. Backlogs grow while urgent cases wait in line.
Extraction and Decoding Live in Separate Tools.
Moving a device from access to analysis often means juggling disconnected software, manual handoffs and duplicate data entry. Inseyets Streamline connects Inseyets.UFED extraction directly to Inseyets.PA decoding in a few clicks.
Not Every Device Needs the Same Attention.
Without a way to prioritize before committing to a full extraction, teams spend hours processing evidence that may not be relevant to the case, delaying the ones that are urgent. Triage and Quick View surface what matters before the clock runs out.
Evidence Has to Survive Scrutiny.
Manual reporting and inconsistent documentation put chain of custody, and case outcomes, at risk. Inseyets generates standardized, defensible reports built to hold up with investigators, prosecutors and the court.
Growth Demands Automation, Not More Headcount.
Larger labs and organizations can’t scale by adding staff alone. Inseyets Autonomy automates decoding and reporting across ten or more endpoints, so teams can process more cases without growing headcount.
One Suite, Every Sector
That Can’t Afford to Wait
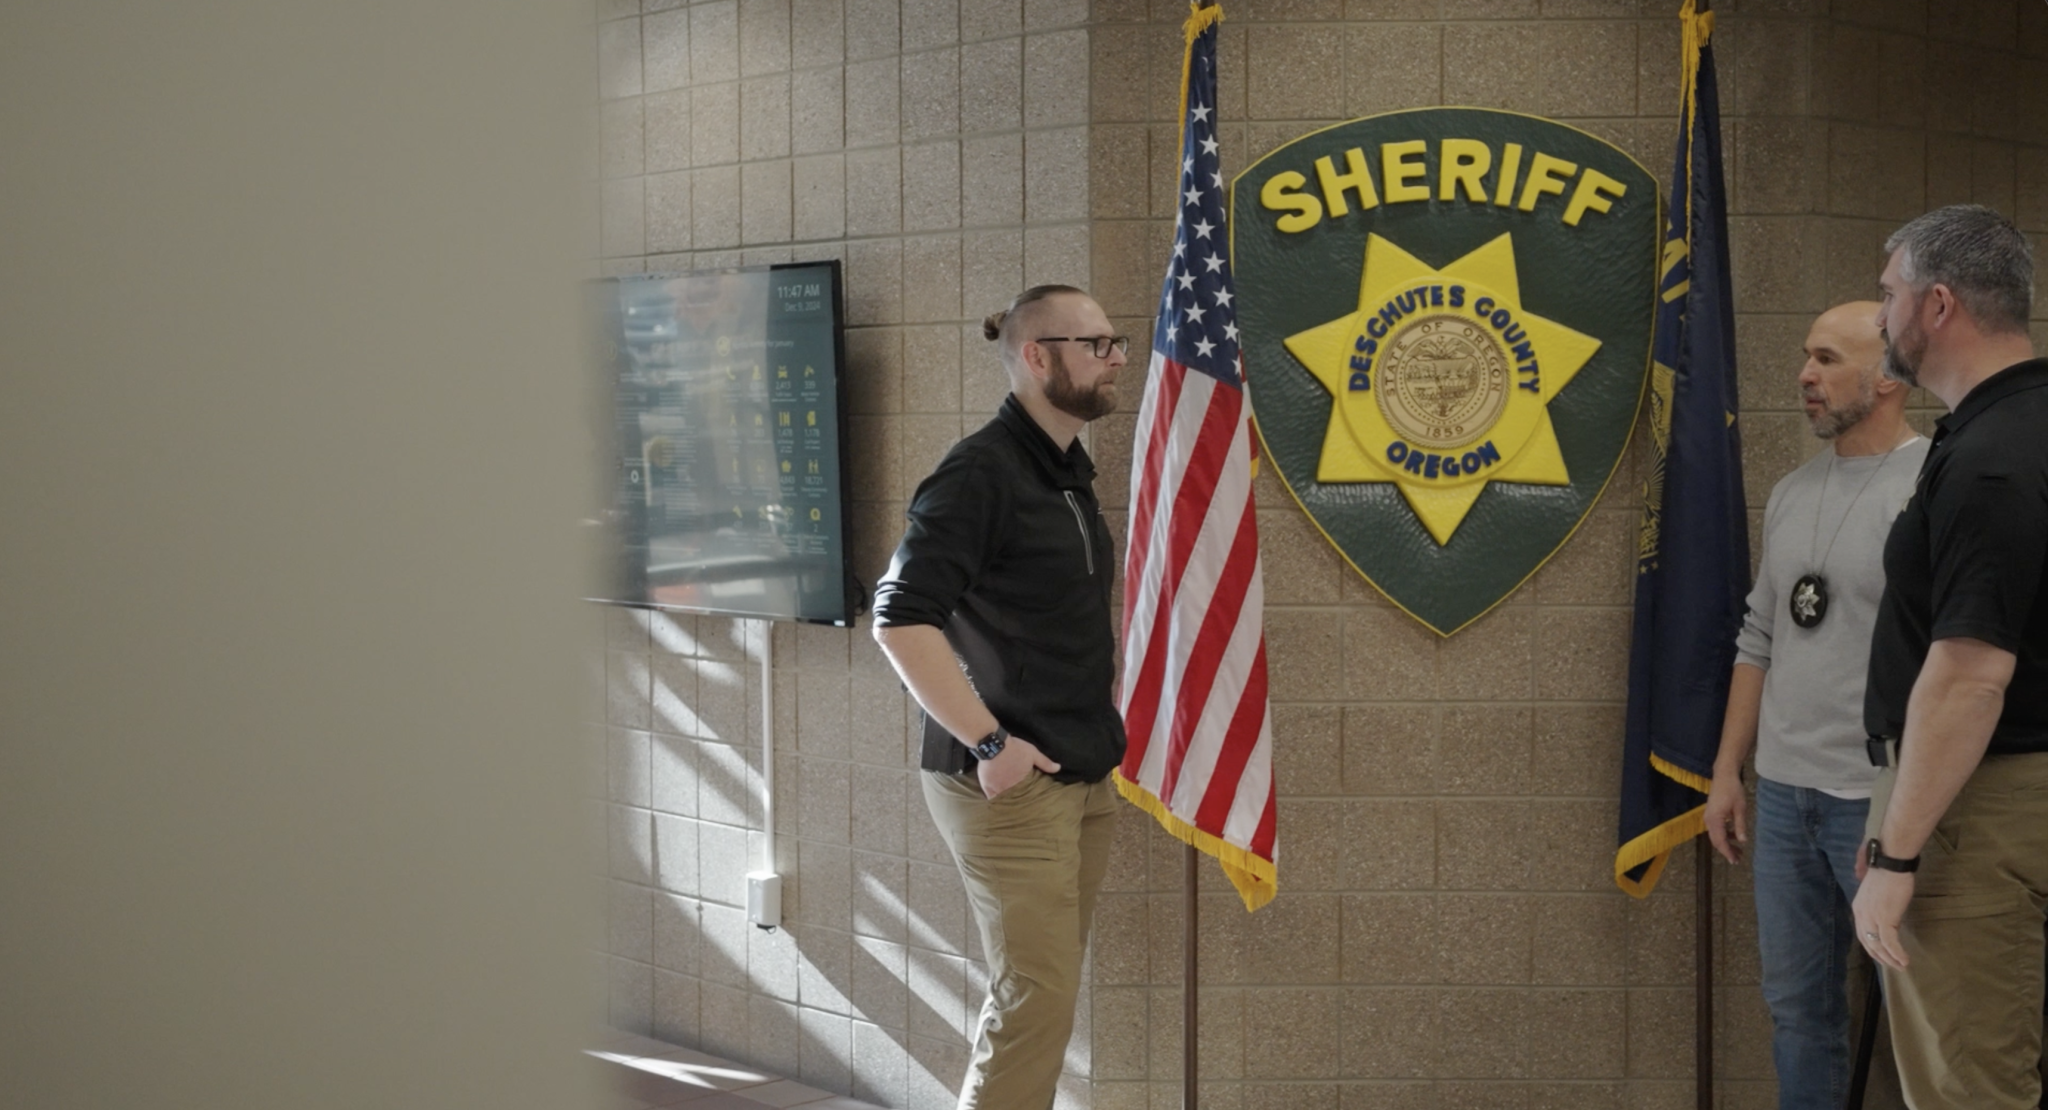
Public Safety
Digital evidence is now central to nearly every case, and caseload continues to outpace the team. Inseyets gives law enforcement, corrections and border agencies the access, extraction and reporting to move from seized device to court-ready evidence fast, without sacrificing the chain of custody a conviction depends on.
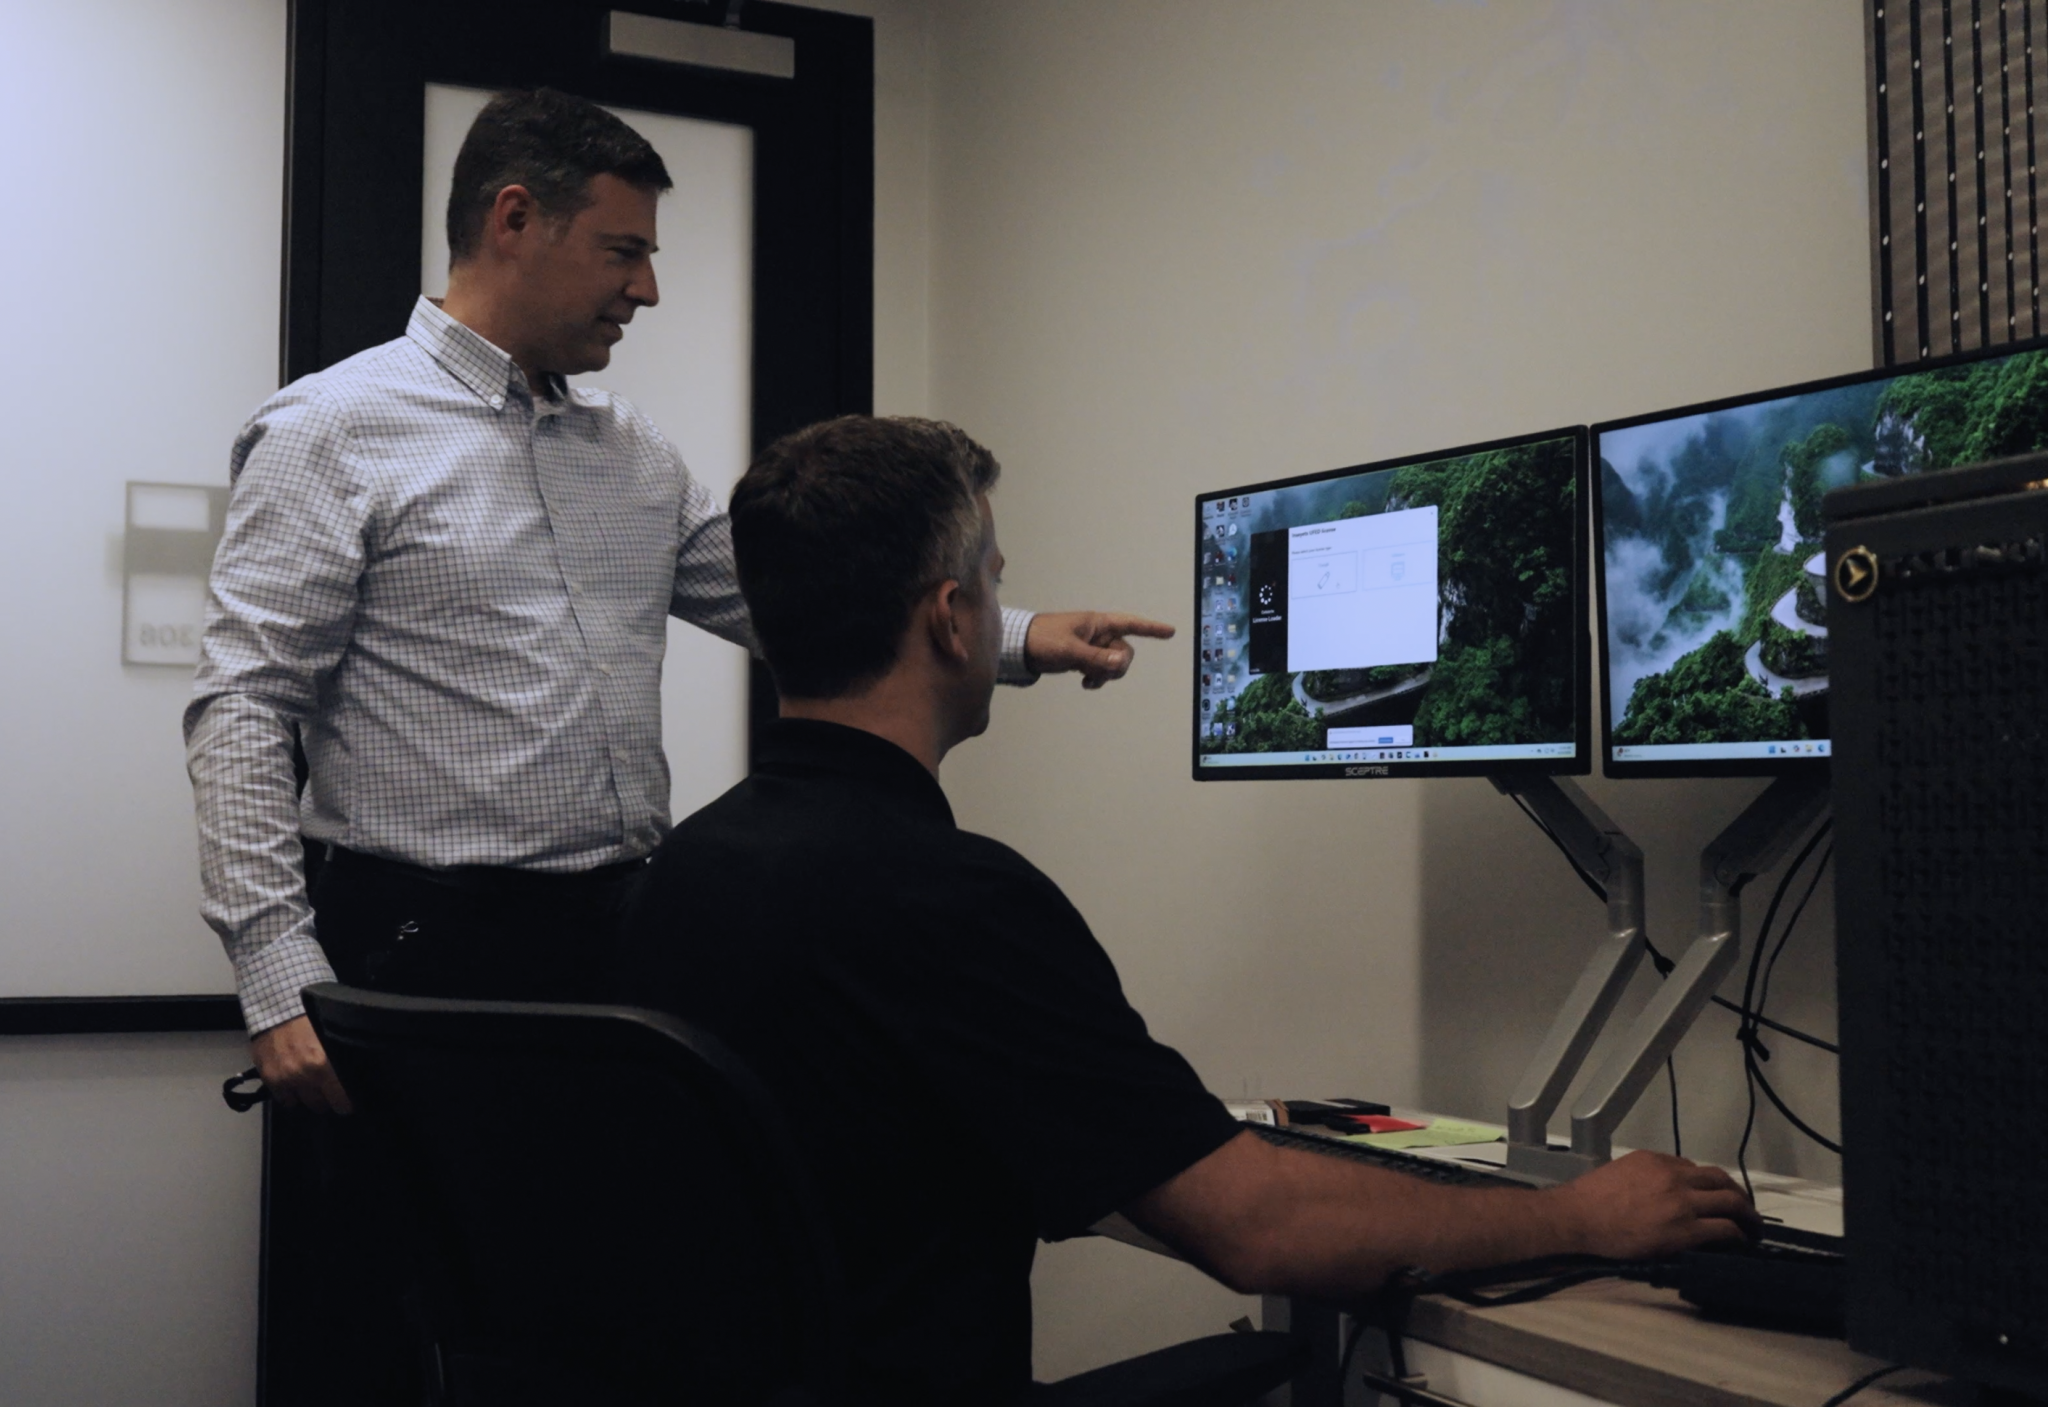
Enterprise
Departing-employee cases, data theft and network exploits don’t wait for a lab. Inseyets gives corporate investigators, eDiscovery and incident response teams the same remote collection and deep-analysis capabilities public-sector labs rely on, so cases are resolved on evidence, not guesswork, before they become bigger liabilities.
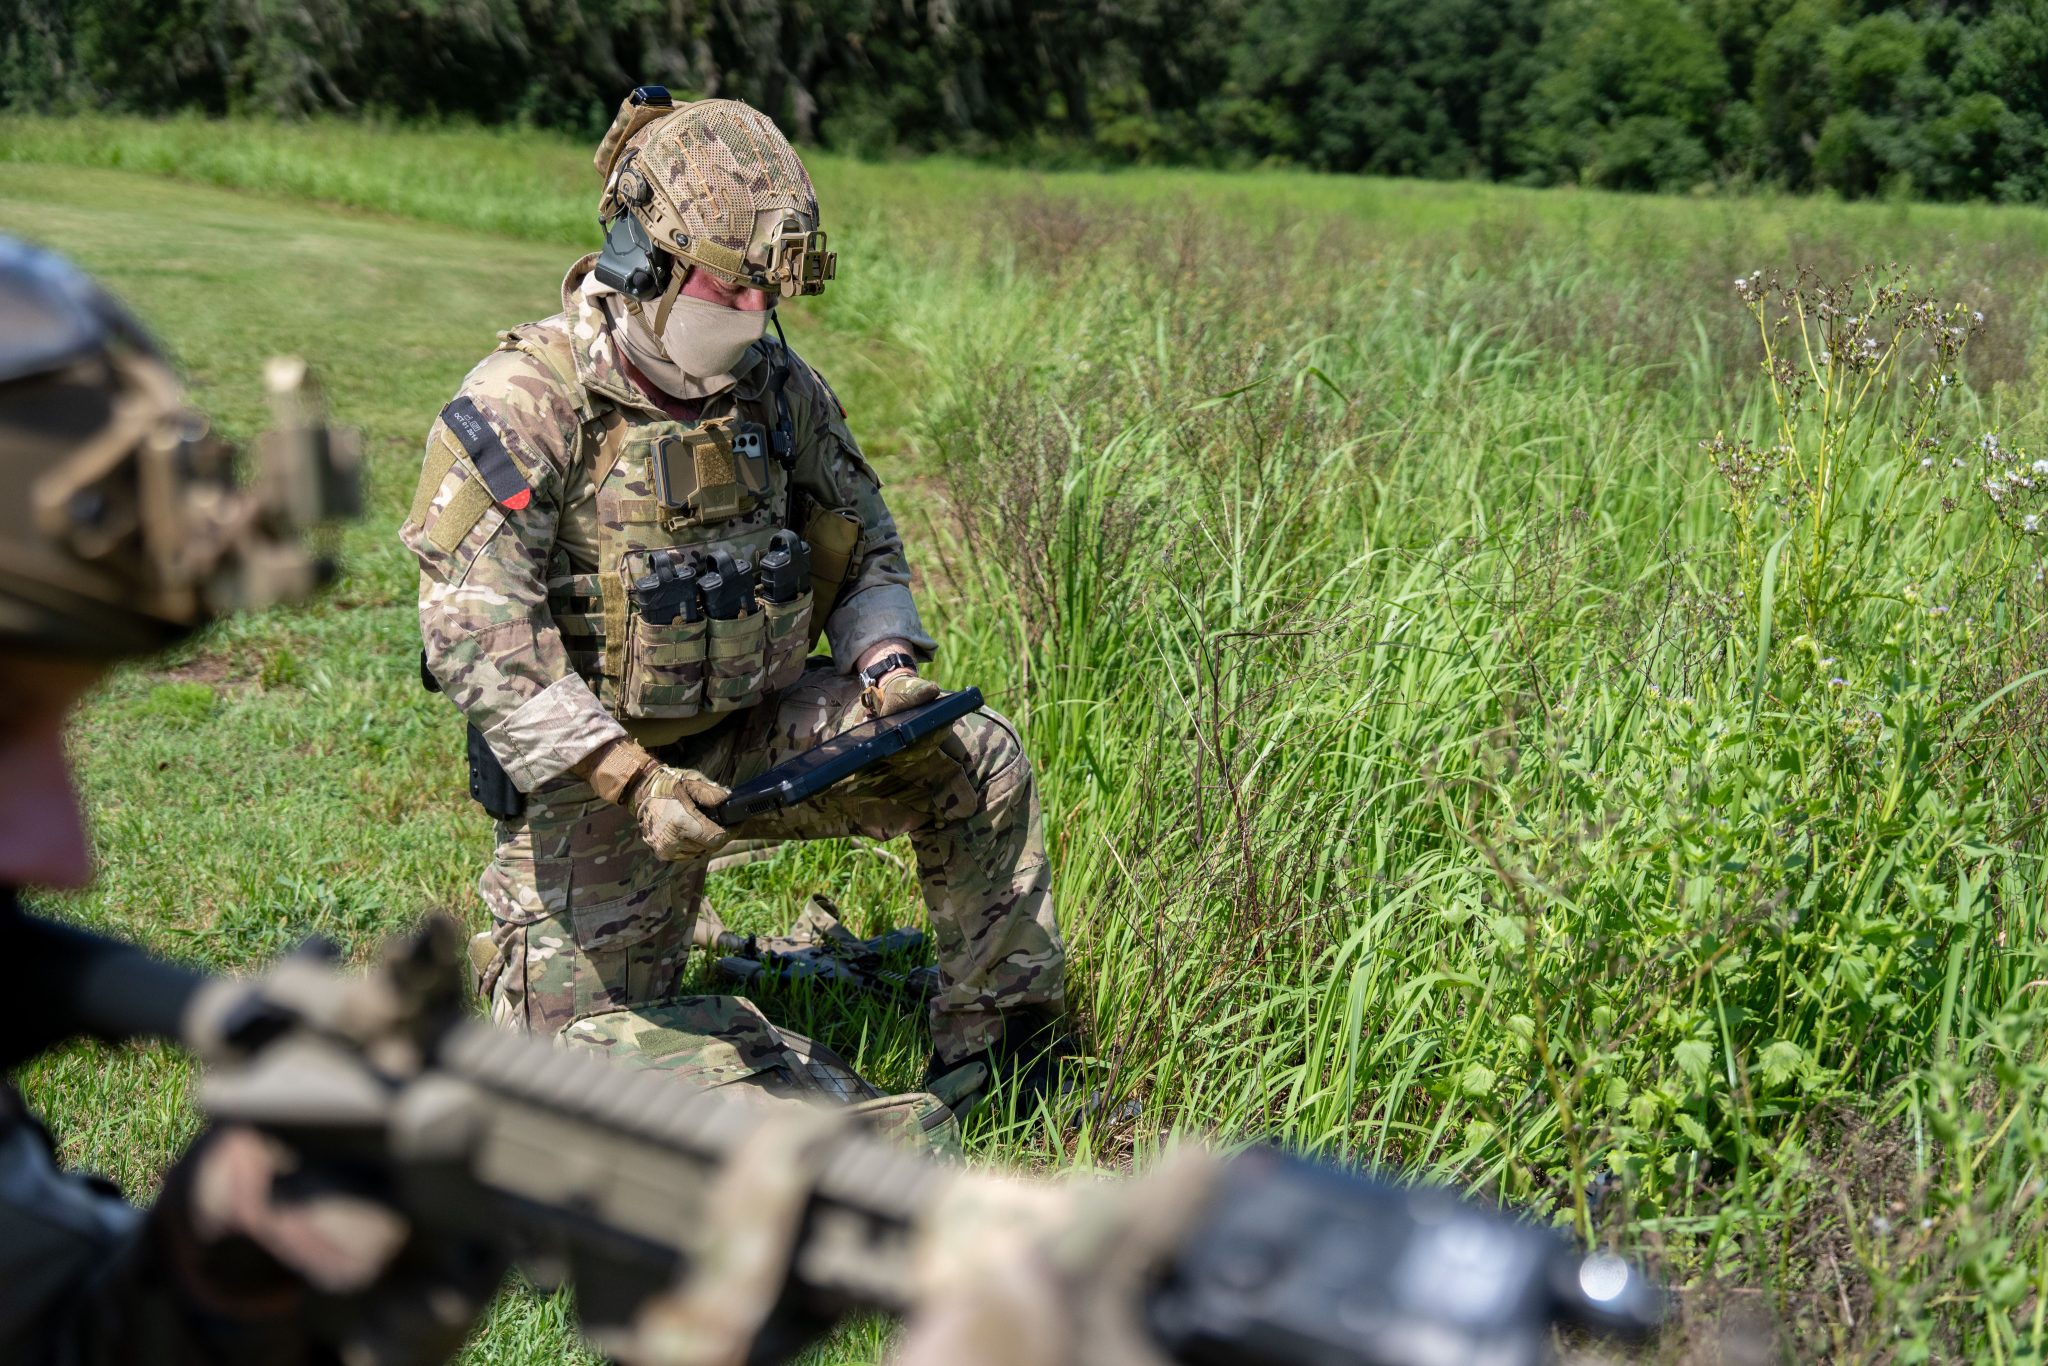
Defense & Intelligence
Mission-critical intelligence has a shelf life, and the point of capture is rarely a lab. Inseyets extracts, decodes and correlates evidence in forward-operating and air-gapped environments, turning raw device data into actionable intelligence and mapping threat networks before they can adapt.
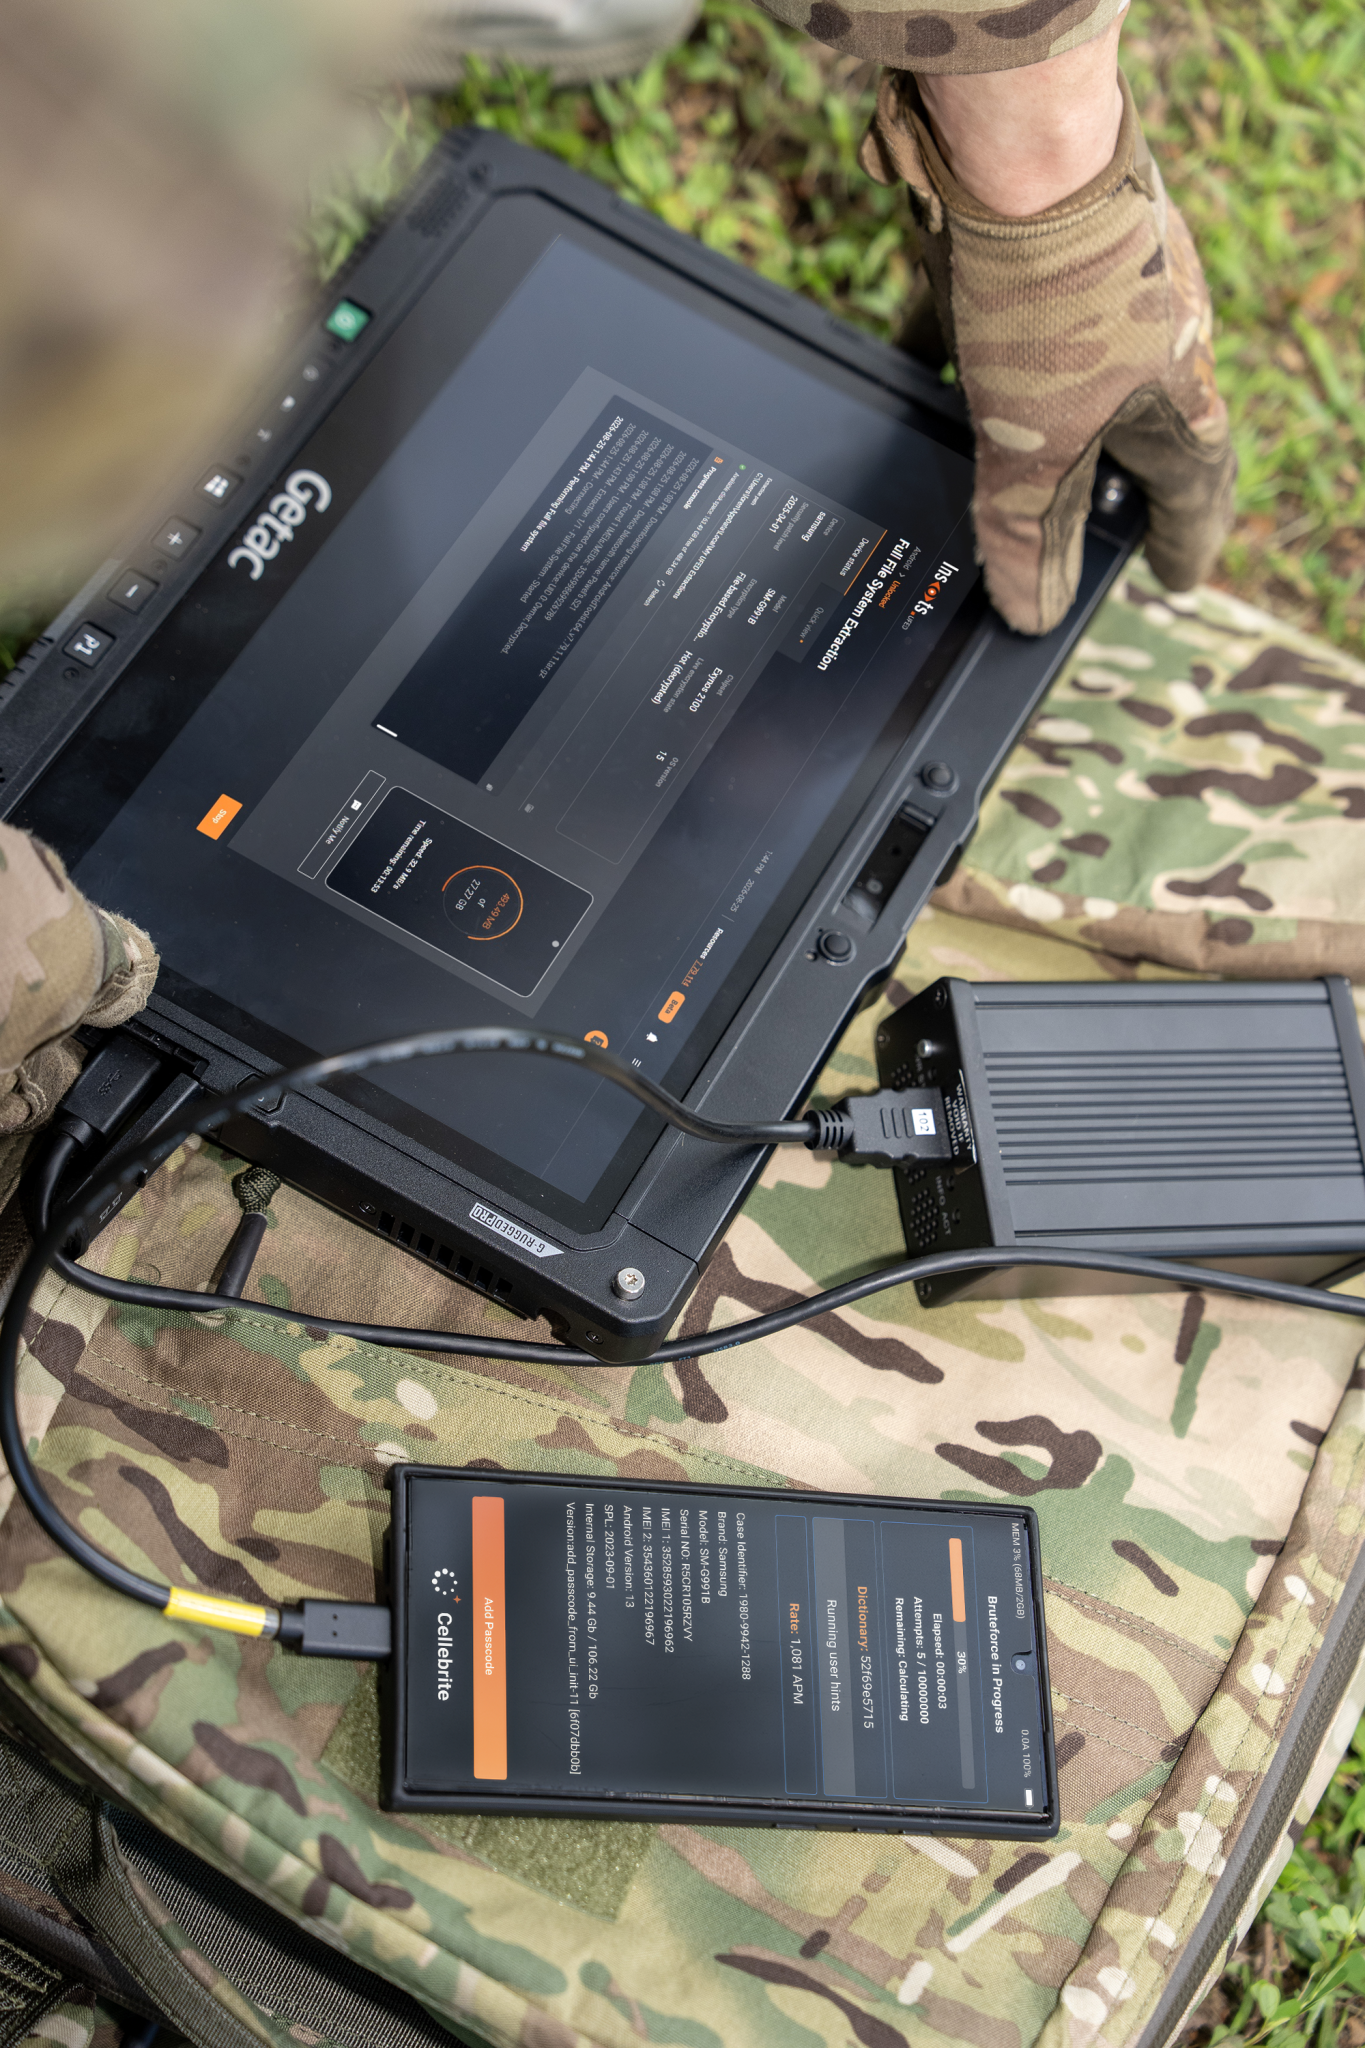
The Power of the Inseyets Suite
Deep Access & Extraction (Inseyets.UFED)
Full File System extraction from the widest range of iOS and Android devices. 5X broader device access than competing tools, departments.
Advanced Decoding & Analysis (Inseyets.PA)
Decode and analyze evidence across 40,000+ app profiles with AI-assisted review, geolocation mapping, SQLite Wizard, Python scripting, App Genie, hex highlighting and court-ready reporting.
Cloud Collection (UFED Cloud)
Collect evidence from 70+ cloud sources, including ephemeral and encrypted messaging, with the same forensic integrity as device extraction.
Streamlined Workflows (Streamline)
Move a device from extraction to a finished UFDR report in a few clicks, without switching tools or re-entering data.
Triage & Quick View
Preview a device before extraction and flag relevant devices using customizable search criteria, so examiners prioritize the cases that can’t wait.
Automated Scale (Cellebrite Autonomy)
Run multiple extraction and analysis workflows simultaneously across ten or more endpoints — scaling lab throughput without scaling headcount.
Collaboration & User Management
(Reader, Commander)
Share case findings with authorized stakeholders across agencies and organizations without breaking chain of custody, and manage permissions, software versions and license allocation across your entire organization, including air-gapped and distributed deployments.
Every Environment, From Lab to Line
Inseyets powers the full range of Cellebrite hardware — from station-based kiosks for self-service extraction to ruggedized field devices built for the most demanding operational environments.
Covert Forensic Imaging Device (CFID)
Palm-sized and battery-powered for forward-operating environments. UAV/drone capable, with SIM card extraction, iOS and Android support and VPN connectivity — built for missions where the lab can’t come to you. Link:
Learn More About CFIDCellebrite Tactical Extraction Kit (C-TEK)
Field-Ready Bundle Ruggedized, mission-ready package for forward-operating defense that combines Inseyets-powered extraction hardware, cables and charging accessories configured for rapid deployment in harsh and disconnected environments.
Learn More About C-TEKCellebrite Kiosk
Self-Service Station Brings the full Inseyets extraction and decoding capabilities to frontline officers with no forensics background. Deployed in law enforcement, corrections and border environments for simple, guided mobile device extraction in minutes.
Learn More About KioskFly Away Kits
Rapid Response Kit Self-contained, airline-transportable deployment kits for rapid response teams and surge capacity deployments. Everything needed to stand up full Inseyets extraction capability at any location, in hours, not days. Details coming soon.
Inseyets Is the Core of the Cellebrite Digital Investigation Platform
Agencies and enterprises already running Cellebrite solutions extend their investigative reach without adding new workflows or infrastructure.
Guardian
Manage evidence, chain of custody and cross-team collaboration from Inseyets processing through case closure.
Pathfinder
Correlate Inseyets data with mobile and digital evidence across cases to surface leads and identify networks.
Genesis
Review digital evidence, surface relevant leads, connect information across multiple evidence sources and move through cases faster with Cellebrite’s AI-powered investigation solution.
Cellebrite Inseyets in Your Region
In North America, the Caseload Outpaces the Lab
Every additional encrypted app, cloud account and gigabyte of seized data adds hours to an investigation already running behind. Customs and Border Patrol seized more than 100 million lethal doses of fentanyl along the southwest border in the first six months of 2026 — and the phone in a suspect’s pocket often holds the route, the contacts and the payment trail that ties the case together, if it’s processed before the trail goes cold.
A Lead That Expires
A South Carolina State Grand Jury prosecution resulted in life-without-parole sentences in June 2025 for two inmates who ran a 630-kilogram methamphetamine trafficking ring entirely from behind bars, coordinated by a contraband cellphone. A seized device is only a lead for as long as it takes to process it — Inseyets.UFED and Inseyets.PA move a device from seizure to evidence without the wait.
Evidence That Holds in Court
In one of the world’s most litigious legal systems, intelligence that can’t survive a suppression motion doesn’t hold. Inseyets produces standardized, CJIS-aligned reporting built to withstand defense scrutiny, turning a seized device into a conviction that sticks.
Scale Without the Headcount
Inseyets is trusted by 93% of U.S. federal departments, and Autonomy lets labs running ten or more endpoints keep pace with caseloads growing faster than their staff. Agencies from Broward County Sheriff’s Office to Calcasieu Parish report turning six-month backlogs into three-week turnarounds.
From a county sheriff’s office to a federal task force, the workflow doesn’t change — the evidence still has to hold.
Faster Across EMEA. Defensible From Case to Conviction.
Since 18 August 2026, the EU’s e-Evidence Regulation has put a hard clock on cross-border evidence: 10 days, eight hours in an emergency. Across EMEA, that is now the pace of the work. Inseyets closes the gap across the whole evidence lifecycle, not just the extraction.
One Case. Many Legal Systems. One Standard.
Collection is where cases are won or lost. Inseyets performs targeted, on-scene extraction — taking what the authorisation covers and leaving what it does not — so examiners meet the data minimisation and purpose limitation duties that Directive (EU) 2016/680 places on member states and Part 3 of the UK Data Protection Act 2018 mirrors. The same method holds in Lyon, Manchester or Abu Dhabi. Faster triage, a smaller lawful footprint, and fewer devices held longer than they need to be.
Compliant From Scene to Disclosure
Evidence that cannot be accounted for cannot be used. Commander governs how extractions are deployed, authorised and logged across distributed units. Guardian carries the case forward through review, sharing and retention on a continuous, auditable chain of custody aligned to ISO/IEC 27037. And because Inseyets can run on-premises inside the agency’s own environment, data stays where the law requires it — GDPR Article 48 still stands, and a foreign warrant alone does not move personal data to a non-EU authority.
Proven in the Field
Cumbria Constabulary runs Cellebrite Inseyets inside its Digital Forensic Unit, where an extraction contributed to a murder conviction now carrying a life sentence. In a jurisdiction where the Forensic Science Regulator’s Code of Practice is statutory, defensible method is not optional.
The agencies keeping pace are not the ones with the most examiners. They are the ones whose workflow does not change when the case crosses a border.
In Asia-Pacific, Distance and Diversity Are the Adversary
India’s law enforcement agencies serve 1.4 billion people across 28 states and land borders with Pakistan, Bangladesh and Myanmar and most operate without a regional forensic lab within practical reach — a gap INTERPOL’s 2025 Asia and South Pacific Cyberthreat Assessment confirms is widening.
A Continent’s Worth of Ground
At the Thailand-Myanmar border, in the heart of the Golden Triangle, more than 1.6 million crossings were recorded at land checkpoints in the first ten months of 2025. Inseyets puts the same extraction and analysis capability at every point of contact, lab or field.
A Continent’s Worth of Devices
With far greater manufacturer and OS diversity than an iPhone-dominant market, broad device coverage matters more here than almost anywhere else. Inseyets.UFED’s 5x broader device access than competing tools is built for exactly this range, not a narrow set of flagship models.
A Continent’s Worth of Law
Inseyets produces an audit-ready chain of custody built to hold up against Australia’s Privacy Act, Japan’s APPI and India’s DPDP Act without switching tools between jurisdictions. Singapore Police and its Home Team Science and Technology Agency have built their digital investigations strategy around Cellebrite’s platform for years.
The same suite that covers a single national police force scales to a region spanning dozens of legal systems — without asking examiners to relearn the workflow at every border.
In LATAM, Organized Crime Is Already Cross-Border and Mobile
An estimated $5 billion in goods crosses South America’s Triple Frontier between Paraguay, Brazil and Argentina every year, almost none of it legal — one reason INTERPOL now runs digital forensics capacity-building programs across 35 countries in Latin America and the Caribbean.
A Network Run From Inside
Brazil’s PCC has directed drug trafficking and extortion operations across roughly 22 states from inside its own prisons using smuggled phones. That network only becomes visible if the devices seized at the edges get processed, not shelved.
A Case Built on Extraction
Brazil’s Federal Police used Cellebrite digital intelligence to identify the accounts and assets behind one such network, seizing $400 million in assets and 50 tons of cocaine in a nine-country operation. The Civil Police of Rio Grande do Sul has scaled that same approach statewide, deploying more than 40 Cellebrite extraction devices across 33 regions.
Evidence That Survives the Courtroom
“We can trace connections between people and reach the perpetrator of homicides that were previously unsolvable,” says Director Elbert Moreira Neto of Rio Grande do Sul’s cybercrimes unit. Inseyets.UFED and Inseyets.PA’s standardized reporting is built to hold up under regional data protection law, Brazil’s LGPD chief among them.
The same workflow that solves a case also has to survive the courtroom that follows it.
In North America, the Caseload Outpaces the Lab
Every additional encrypted app, cloud account and gigabyte of seized data adds hours to an investigation already running behind. Customs and Border Patrol seized more than 100 million lethal doses of fentanyl along the southwest border in the first six months of 2026 — and the phone in a suspect’s pocket often holds the route, the contacts and the payment trail that ties the case together, if it’s processed before the trail goes cold.
A Lead That Expires
A South Carolina State Grand Jury prosecution resulted in life-without-parole sentences in June 2025 for two inmates who ran a 630-kilogram methamphetamine trafficking ring entirely from behind bars, coordinated by a contraband cellphone. A seized device is only a lead for as long as it takes to process it — Inseyets.UFED and Inseyets.PA move a device from seizure to evidence without the wait.
Evidence That Holds in Court
In one of the world’s most litigious legal systems, intelligence that can’t survive a suppression motion doesn’t hold. Inseyets produces standardized, CJIS-aligned reporting built to withstand defense scrutiny, turning a seized device into a conviction that sticks.
Scale Without the Headcount
Inseyets is trusted by 93% of U.S. federal departments, and Autonomy lets labs running ten or more endpoints keep pace with caseloads growing faster than their staff. Agencies from Broward County Sheriff’s Office to Calcasieu Parish report turning six-month backlogs into three-week turnarounds.
From a county sheriff’s office to a federal task force, the workflow doesn’t change — the evidence still has to hold.
Faster Across EMEA. Defensible From Case to Conviction.
Since 18 August 2026, the EU’s e-Evidence Regulation has put a hard clock on cross-border evidence: 10 days, eight hours in an emergency. Across EMEA, that is now the pace of the work. Inseyets closes the gap across the whole evidence lifecycle, not just the extraction.
One Case. Many Legal Systems. One Standard.
Collection is where cases are won or lost. Inseyets performs targeted, on-scene extraction — taking what the authorisation covers and leaving what it does not — so examiners meet the data minimisation and purpose limitation duties that Directive (EU) 2016/680 places on member states and Part 3 of the UK Data Protection Act 2018 mirrors. The same method holds in Lyon, Manchester or Abu Dhabi. Faster triage, a smaller lawful footprint, and fewer devices held longer than they need to be.
Compliant From Scene to Disclosure
Evidence that cannot be accounted for cannot be used. Commander governs how extractions are deployed, authorised and logged across distributed units. Guardian carries the case forward through review, sharing and retention on a continuous, auditable chain of custody aligned to ISO/IEC 27037. And because Inseyets can run on-premises inside the agency’s own environment, data stays where the law requires it — GDPR Article 48 still stands, and a foreign warrant alone does not move personal data to a non-EU authority.
Proven in the Field
Cumbria Constabulary runs Cellebrite Inseyets inside its Digital Forensic Unit, where an extraction contributed to a murder conviction now carrying a life sentence. In a jurisdiction where the Forensic Science Regulator’s Code of Practice is statutory, defensible method is not optional.
The agencies keeping pace are not the ones with the most examiners. They are the ones whose workflow does not change when the case crosses a border.
In Asia-Pacific, Distance and Diversity Are the Adversary
India’s law enforcement agencies serve 1.4 billion people across 28 states and land borders with Pakistan, Bangladesh and Myanmar and most operate without a regional forensic lab within practical reach — a gap INTERPOL’s 2025 Asia and South Pacific Cyberthreat Assessment confirms is widening.
A Continent’s Worth of Ground
At the Thailand-Myanmar border, in the heart of the Golden Triangle, more than 1.6 million crossings were recorded at land checkpoints in the first ten months of 2025. Inseyets puts the same extraction and analysis capability at every point of contact, lab or field.
A Continent’s Worth of Devices
With far greater manufacturer and OS diversity than an iPhone-dominant market, broad device coverage matters more here than almost anywhere else. Inseyets.UFED’s 5x broader device access than competing tools is built for exactly this range, not a narrow set of flagship models.
A Continent’s Worth of Law
Inseyets produces an audit-ready chain of custody built to hold up against Australia’s Privacy Act, Japan’s APPI and India’s DPDP Act without switching tools between jurisdictions. Singapore Police and its Home Team Science and Technology Agency have built their digital investigations strategy around Cellebrite’s platform for years.
The same suite that covers a single national police force scales to a region spanning dozens of legal systems — without asking examiners to relearn the workflow at every border.
In LATAM, Organized Crime Is Already Cross-Border and Mobile
An estimated $5 billion in goods crosses South America’s Triple Frontier between Paraguay, Brazil and Argentina every year, almost none of it legal — one reason INTERPOL now runs digital forensics capacity-building programs across 35 countries in Latin America and the Caribbean.
A Network Run From Inside
Brazil’s PCC has directed drug trafficking and extortion operations across roughly 22 states from inside its own prisons using smuggled phones. That network only becomes visible if the devices seized at the edges get processed, not shelved.
A Case Built on Extraction
Brazil’s Federal Police used Cellebrite digital intelligence to identify the accounts and assets behind one such network, seizing $400 million in assets and 50 tons of cocaine in a nine-country operation. The Civil Police of Rio Grande do Sul has scaled that same approach statewide, deploying more than 40 Cellebrite extraction devices across 33 regions.
Evidence That Survives the Courtroom
“We can trace connections between people and reach the perpetrator of homicides that were previously unsolvable,” says Director Elbert Moreira Neto of Rio Grande do Sul’s cybercrimes unit. Inseyets.UFED and Inseyets.PA’s standardized reporting is built to hold up under regional data protection law, Brazil’s LGPD chief among them.
The same workflow that solves a case also has to survive the courtroom that follows it.
Everything You Need to Evaluate
and Deploy Inseyets
The Calcasieu Parish Sheriff’s Office Makes Breakthroughs with Cellebrite’s Digital Investigative Solutions
Read the Story More Devices. More Data.
One Platform to Keep Up.
Every device holds a story. Inseyets gives your team the access,
decoding and workflow to find it faster, and turn it into evidence
that holds up, trusted by 7,000+ public safety, enterprise and
government customers worldwide.
Frequently Asked Questions
Cellebrite Inseyets is a purpose-built, all-inclusive digital forensics suite of solutions powered by the advanced access and extraction capabilities of Premium and UFED, the decoding and analysis capabilities of Physical Analyzer, and new capabilities that streamline, automate and offer other time-saving tools that provide Examiners with the most efficient solution in the Digital Forensics community today.
Products
- Cellebrite Inseyets.UFED – Access devices and data previously unreachable and extract the Full File System data including containerized applications and encrypted data.
- Cellebrite Inseyets.PA – Process and analyze evidence quickly from the broadest range of apps and sources, enrich the case with in-depth information and validate your evidence easily.
- Cellebrite Reader – Review evidence thoroughly, use advanced search, filtering, timeline, entity bookmarks and project saving features to find key details and capture review progress.
Features
- Cellebrite Streamline – Easily and quickly process a device from extraction to UFDR in a few clicks.
- Cellebrite Quick View – Get a glimpse into the device before extraction and help identify the device’s relevance and priority.
- Cellebrite Triage – Leverage customizable search criteria to quickly flag relevant devices and significantly improve device prioritization.
- Cellebrite UFED Cloud – Extract, preserve and analyze cloud-based data using device-based tokens or known credentials and gain access to valuable evidence that is not available on the device.
- Cellebrite Commander – Manage permissions and capabilities for all users, including software updates and license updates.
Add-ons
- Cellebrite Autonomy – Scale-up investigations and run multiple automated processes quickly and accurately at once.
- Cellebrite Unlocks – Access locked devices to lawfully extract critical information from a broad range of devices.
When upgrading to Cellebrite Inseyets, you will enjoy these added capabilities:
- UFED customer – Advanced device access, including unlock-ready, Full File System extractions, Streamlined workflows, Quick Views before full extraction, Triage prioritization, Automated multi-processing capabilities, Cloud-account access, Commander and more.
- Premium customer – Streamlined workflows, Quick Views before full extraction, Triage prioritization, Automated multi-processing capabilities, Cloud-account access, Commander and more.
To take full advantage of Cellebrite Inseyets, a connection to a network is required (there is no exchange of device data). Cellebrite Inseyets is also available as an offline configuration to match your agency’s needs. We advise following Cellebrite Inseyets security requirements to prepare your workstation.
We will be transitioning all users to Cellebrite Inseyets and discontinuing the following products:
- UFED Ultimate (UFED4PC & Physical Analyzer)
- Physical Analyzer 7
- Premium
- Premium Enterprise
- Premium SaaS
- Commander for UFED4PC
- Cloud Analyzer
This change is being made to enhance and simplify your overall experience with the product portfolio.
Inseyets is unlock-ready, however you need to purchase the unlocks package separately.
Turbo Link serves as the advanced connection between the device and the capabilities of the solution. It embodies the cutting-edge technology powering Cellebrite Inseyets, enhancing the speed and efficiency of data extraction and analysis (formerly known as the “Cheetah” adapter).
Some systems may require additional hardware. Please refer to the product technical sheets for the specific details.
Cellebrite Inseyets requires a Cellebrite Max dongle. (Check your dongle type here)
Cellebrite Inseyets.PA (version 10.x), operates on a database that handles large volumes of data. It introduces new features like Geo-Location Semantics, Media Origin, Import/Export and quicker case reopening. With the new Cellebrite Inseyets offering, you will also enjoy additional enhancements like Cloud and Crypto features. (Cellebrite Inseyets.PA and PA 7, share the same decoding abilities)
You may explore Cellebrite Inseyets powered by PA v10.x, however, please be aware that you will only be able to utilize the decoding and analysis features. The rest of Cellebrite Inseyets capabilities such as extraction and other advanced capabilities will not be available to try.


